🟠 𝗛𝗜𝗚𝗛 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝗶𝗙𝗶𝗻𝗸 👤 Actor: qilin Threat actor 'qilin' claims iFink as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI t.co/JISllf1NjE

- 0 réponses
- 0 partages
- 0 j'aime
- 24 vues
Rose Griffon, les comptes officiels du jeu et LEVEL-5, sur X, Instagram, TikTok et YouTube.
🟠 𝗛𝗜𝗚𝗛 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝗶𝗙𝗶𝗻𝗸 👤 Actor: qilin Threat actor 'qilin' claims iFink as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI t.co/JISllf1NjE
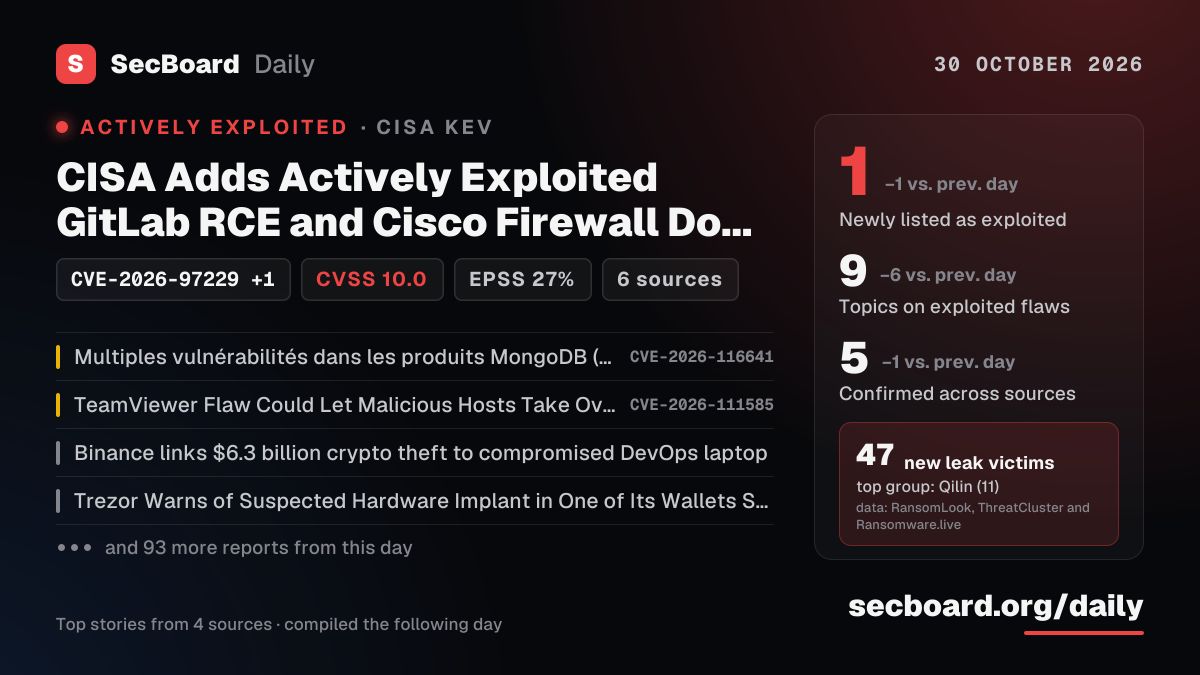
SecBoard Daily · 30 October 2026 Top story: CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEV (CVE-2026-97229, actively exploited) 1 newly listed as exploited Full daily briefing on SecBoard – address in the image. #ThreatIntel #GitLab t.co/BdNAB66pCC
Just receiving a RAR was enough: MDaemon's ClamAV scan dropped a backdoor DLL on mail servers in Ukraine. t.co/WtUDzNxmA9 #ThreatIntel #CVE_2025_8088 #HELLAGE #HELLTAG t.co/XDnRUq7udc
#ThreatIntelligence #Thread #ThreatIntel t.co/osT2sf82uN

Unauthenticated email can plant stored XSS in RT/RTIR tickets - aimed at the analysts who triage them. t.co/3CfoPRBBgS #ThreatIntel #CVE_2026_105454 #CVE_2026_105455 t.co/GWP3G2f76v
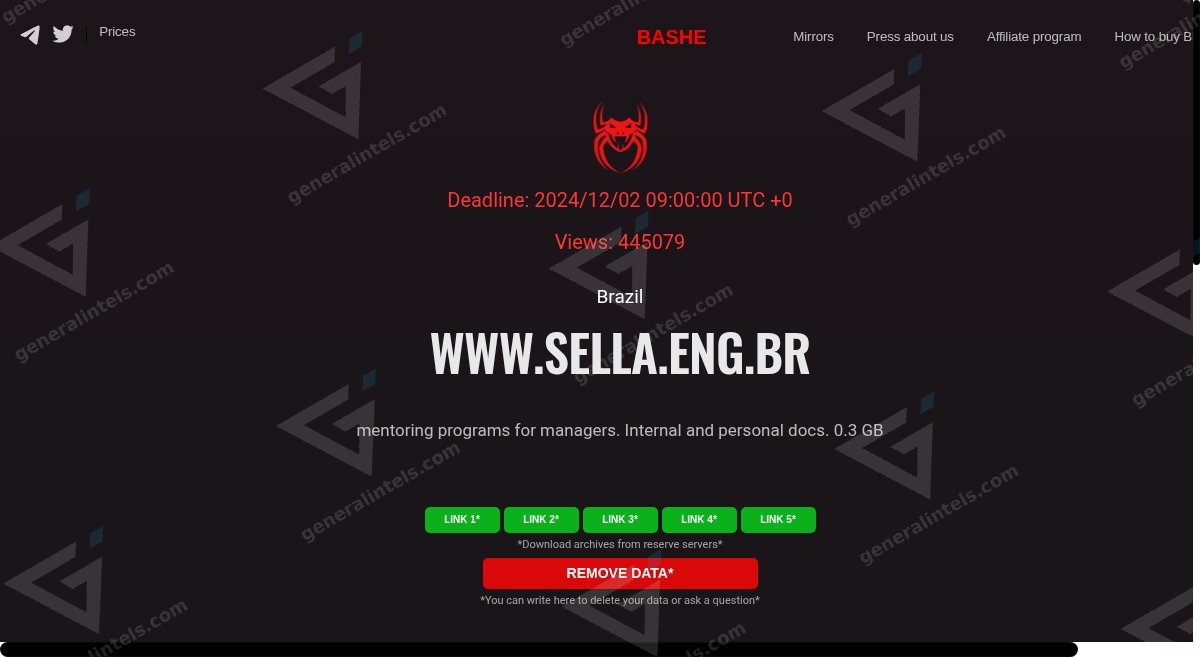
🟠 𝗛𝗜𝗚𝗛 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝘀𝗲𝗹𝗹𝗮.𝗲𝗻𝗴[.]𝗯𝗿 👤 Actor: apt73 Threat actor 'apt73' claims sella.eng[.]br as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI t.co/a8axdwBUJE
Hyper-V internals deep dive: VMBus, vmwp and the guest-to-host attack surface, mapped for defenders. t.co/blUMa9Sb2B #ThreatIntel #IDA #BinDiff #Diaphora t.co/3zgbmHQOUe
Two public, stable PoCs take a Windows minifilter N-day from user or admin straight to SYSTEM. t.co/oBGBuJ43me #ThreatIntel #IDA t.co/LOdwEXfR5Z
🟠 𝗛𝗜𝗚𝗛 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝗻𝗲𝘁𝗿𝗼𝗺𝘀𝗼𝗳𝘁𝘄𝗮𝗿𝗲[.]𝗿𝗼 👤 Actor: apt73 Threat actor 'apt73' claims netromsoftware[.]ro as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI t.co/kOBUcxrtSq

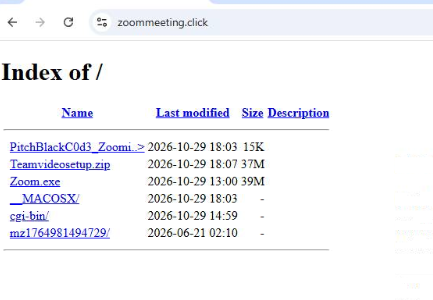
zoommeetingconnect[.]click @spaceship #ThreatIntel #Phishing t.co/cnFfgxg3ox


zoommeeting[.]click #Phishing #ThreatIntel t.co/pumlTYbvw5
New public chains turn a patched Windows cldflt.sys bug into PPL-stripped LSASS credential theft. t.co/ZjVTcLwJon #ThreatIntel #CVE_2024_30085 #Windows10 #Metasploit t.co/dn6bgtNCYT
🔴 𝗖𝗥𝗜𝗧𝗜𝗖𝗔𝗟 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝗳𝗽𝗷.𝗰𝗼𝗺[.]𝗽𝘆 👤 Actor: apt73 Threat actor 'apt73' claims t.co/HO34PpsYdZ[.]py as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI
64% of secrets valid in 2022 still work today - leaked credentials rarely get rotated. t.co/A4V3kiEQ9f #ThreatIntel #ShaiHulud #TruffleHog #Secrets t.co/DHA2Io9YWC
One leading // in a path and Faraday sends your Ruby service's request to the attacker's host. t.co/dp6sKj0Pmg #ThreatIntel #CVE_2026_25765 #Ruby #httpclient t.co/fLpmLXpC3w
🔴 𝗖𝗥𝗜𝗧𝗜𝗖𝗔𝗟 · 𝗖𝗹𝗮𝗶𝗺𝗲𝗱 𝘃𝗶𝗰𝘁𝗶𝗺 𝗹𝗶𝘀𝘁𝗶𝗻𝗴 🏢 Attributed to: 𝗮𝗹𝗶𝗼𝗿𝗯𝗮𝗻𝗸[.]𝗽𝗹 👤 Actor: apt73 Threat actor 'apt73' claims aliorbank[.]pl as a victim. Unverified claim. #DataLeak #ThreatIntel #CTI t.co/OlzKjprniL

An AI agent proved 22 CVEs in 13 self-hosted tools - Crawl4AI is an unauthenticated 10.0 RCE. t.co/szTX47szMp #ThreatIntel #CVE_2026_28357 #CVE_2026_28359 #ProjectDiscovery t.co/lchFaWhl0g
Langflow was exploited within hours of disclosure - now KEV-listed CVEs get open Nuclei checks. t.co/kvUS93aW1B #ThreatIntel #CVE_2026_41940 #CVE_2026_33017 #Nuclei t.co/HQFE3hNbKL
🔒 #CyberSecurity CVE-2026-97229: Critical GitLab RCE Exploited Against Alpine Linux — Detection … "A maximum-severity vulnerability in GitLab, tracked as CVE-2026-97229, is being actively…" 🔗 t.co/fWZ68FFt7W #CyberSecurity #ThreatIntel #cve #zeroday #patchtuesday
🔒 #CyberSecurity WordPress Core Unauthenticated RCE: 63,000 Attack Attempts in 24 Hours — Detect… "In the world of vulnerability management, there are patching windows, and then there are…" 🔗 t.co/C5S0HrMtUP #CyberSecurity #ThreatIntel #critical #zeroday #cve
X est relu en direct toutes les 30 secondes : profils, fils, recherche et conversations.
YouTube (flux public des chaînes), TikTok (les dernières vidéos publiques) et Instagram (la grille publique des profils) sont synchronisés en tâche de fond toutes les 30 minutes. Sans connexion, TikTok et Instagram se limitent à leurs publications les plus récentes, sans likes ni commentaires pour Instagram.
Aucun compte officiel d'Inazuma Eleven ou de LEVEL-5 n'est référencé sur Instagram ni TikTok ; leurs vidéos officielles sont sur la chaîne YouTube LEVEL5ch.